<img height="1" width="1" style="display:none;" alt="" src="https://px.ads.linkedin.com/collect/?pid=4668217&amp;fmt=gif">

AI Agents for Customer Service See more

SECURITY & COMPLIANCE

Secure, controlled and compliant by design

Schaman is built to meet the security, privacy and regulatory requirements of enterprise environments — ensuring that customer data, system access and AI-driven decisions are protected, controlled and auditable at all times.

Talk to an expert
Hero Scurity and Compliance

BUILT FOR CONTROL, AUDITABILITY AND REGULATORY COMPLIANCE

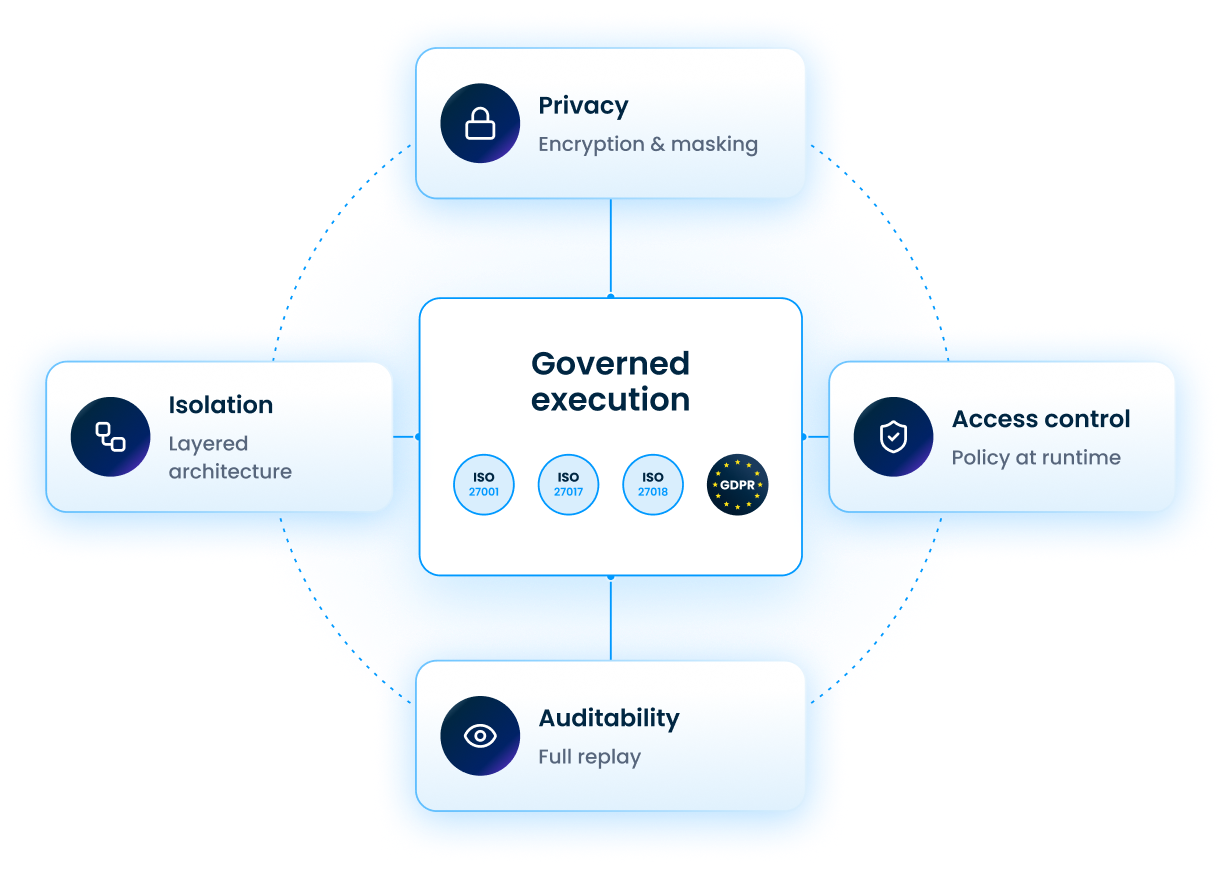
Security embedded across the entire architecture

Security in Schaman is not limited to access control or data protection. It is embedded across the entire architecture — governing how data is accessed, how decisions are made and how actions are executed.

Outline Icon (10)

Protect customer data across all interactions

High Agent Turnover & Fluctuating Contact Volumes

Outline Icon (2)-1

Enforce control at every step of execution

Apply policy-driven controls to every data query and system action — ensuring that all operations comply with defined security and governance rules in real time.

Outline Icon (1)-1

Operate within regulatory frameworks

Support compliance with key regulations and standards, ensuring alignment with data protection and AI governance requirements.

Outline Icon (3)

Maintain full auditability and traceability

Track and reconstruct all interactions, decisions and execution steps — enabling complete visibility for compliance, validation and analysis.

A CONTINUOUS SECURITY AND COMPLIANCE MODEL

Protect, control, audit, improve

Schaman ensures that security and compliance are continuously enforced, monitored and refined across all operations.

DATA PROTECTION & PRIVACY

Protect sensitive customer data by design

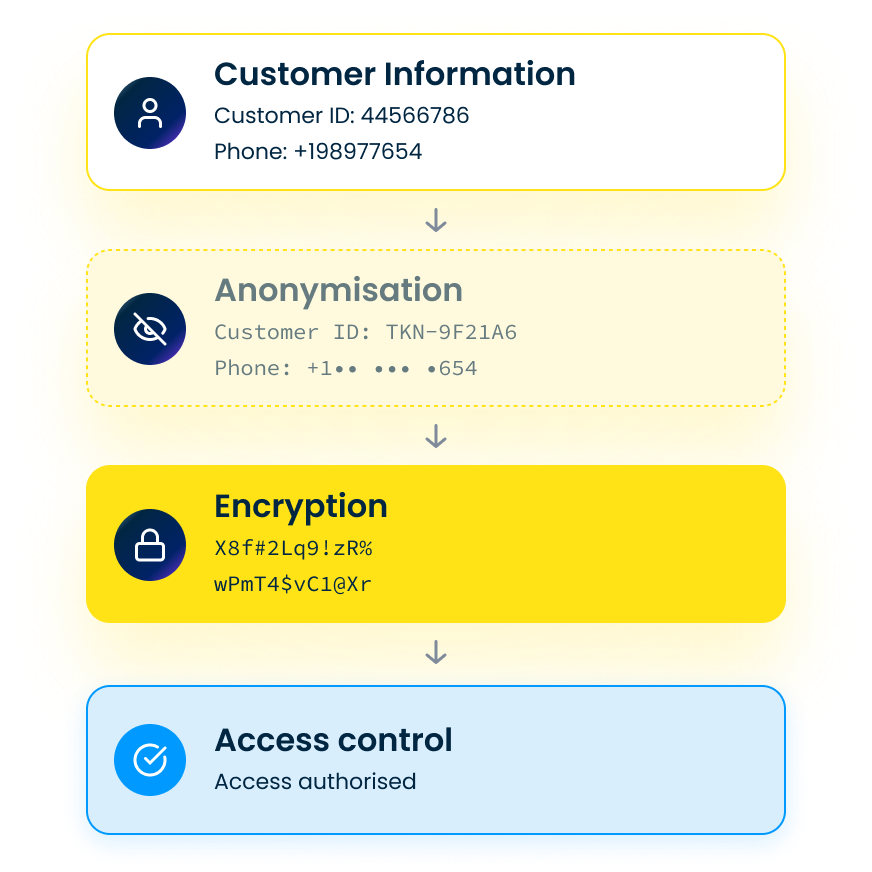
Schaman applies encryption in transit and at rest, strict access controls and data minimisation principles to ensure that sensitive customer data is protected at all times.

It supports compliance with:

GDPR ISO 27001 ISO 27017 ISO 27018
Frame 1139
POLICY-DRIVEN ACCESS CONTROL

Control access at runtime,
not just at entry points

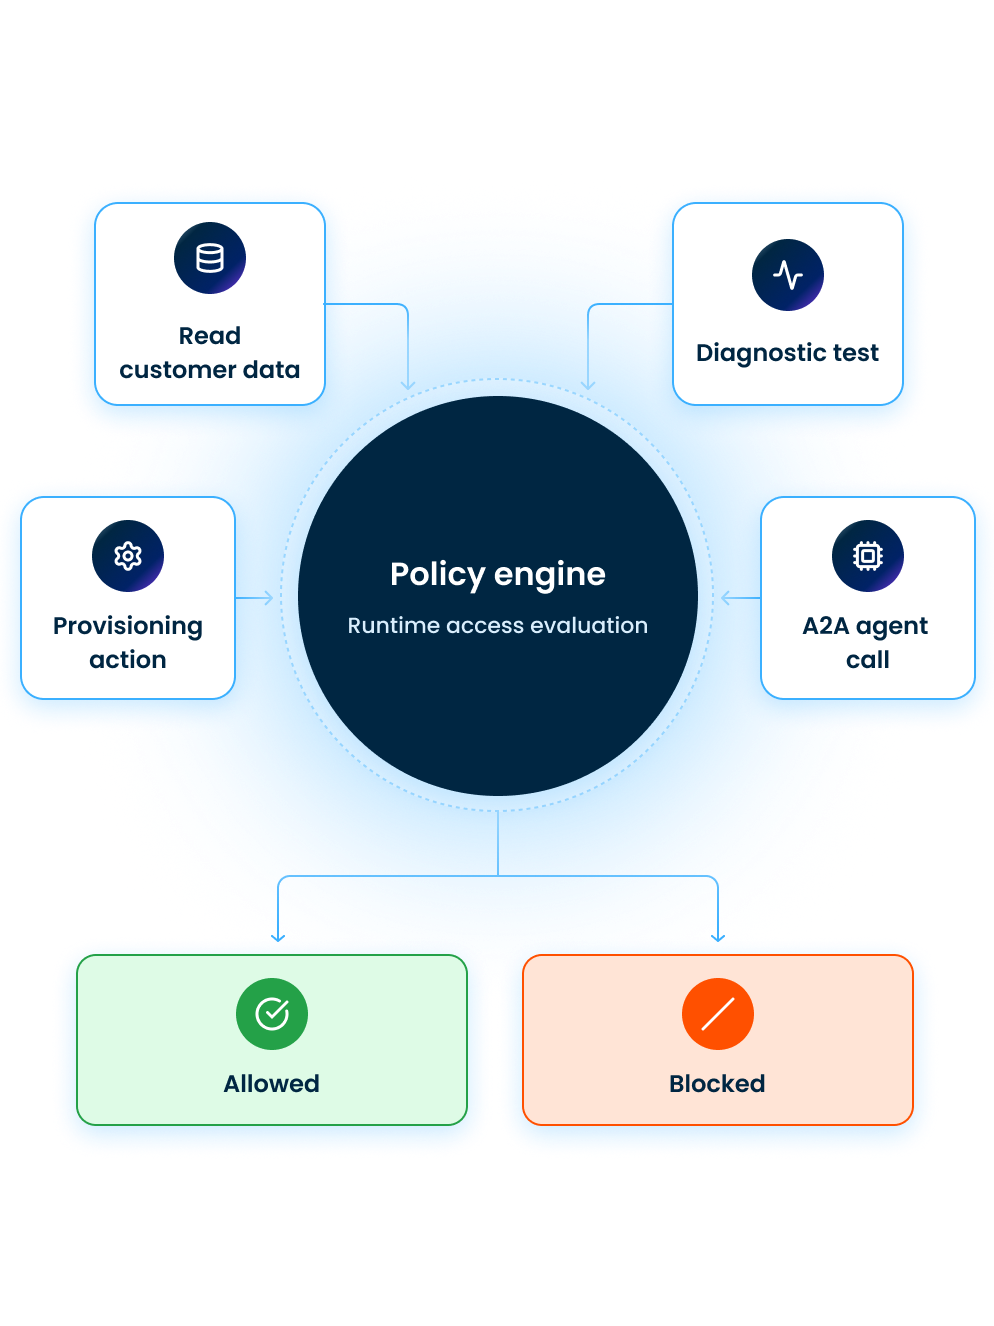
Schaman enforces access policies dynamically across all interactions — ensuring that every data query and system action is authorised in real time, not only at authentication.

Consistent enforcement of governance rules
Reduced risk of unauthorised actions
Fine-grained control across all operations
Image (4)
SECURE-BY-DESIGN ARCHITECTURE

Minimise exposure and isolate critical components

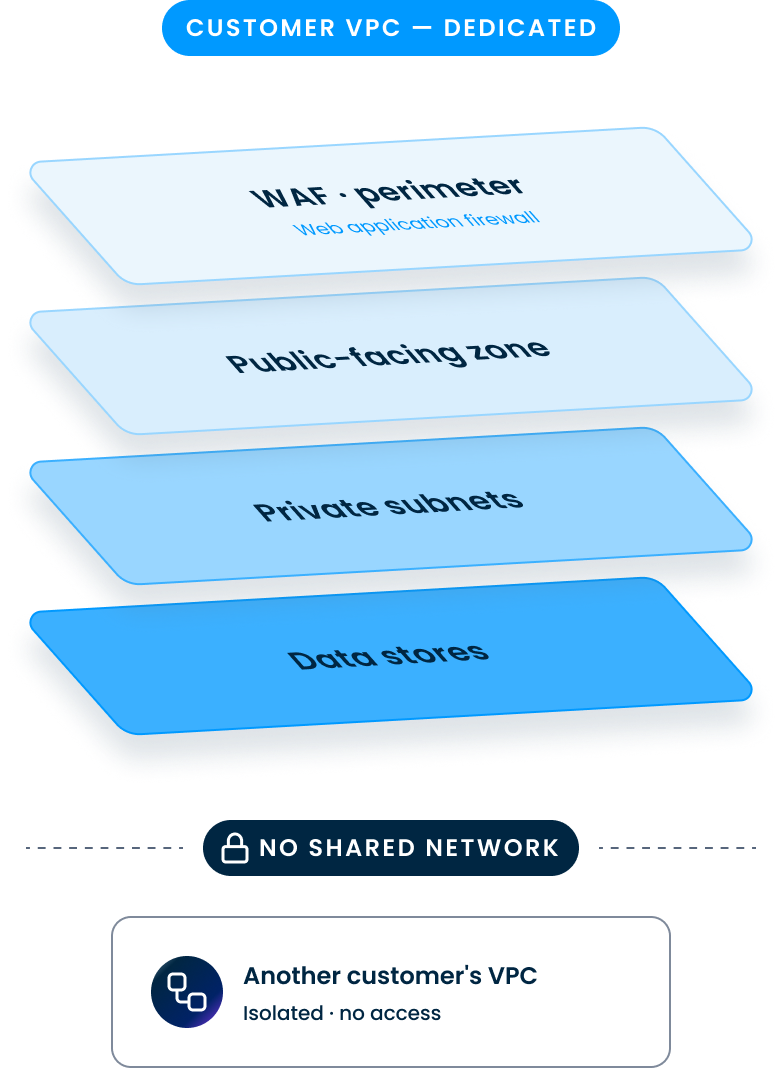
Schaman follows a layered architecture where:

All system access is mediated through secure orchestration proxies
Internal components remain isolated (conversation, orchestration logic, data access)
Direct exposure of underlying systems is avoided

This reduces attack surface and ensures consistent enforcement of security controls.

Dedicated VPC · architecture cutaway
FULL AUDITABILITY & TRACEABILITY

Record and reconstruct every system behaviour

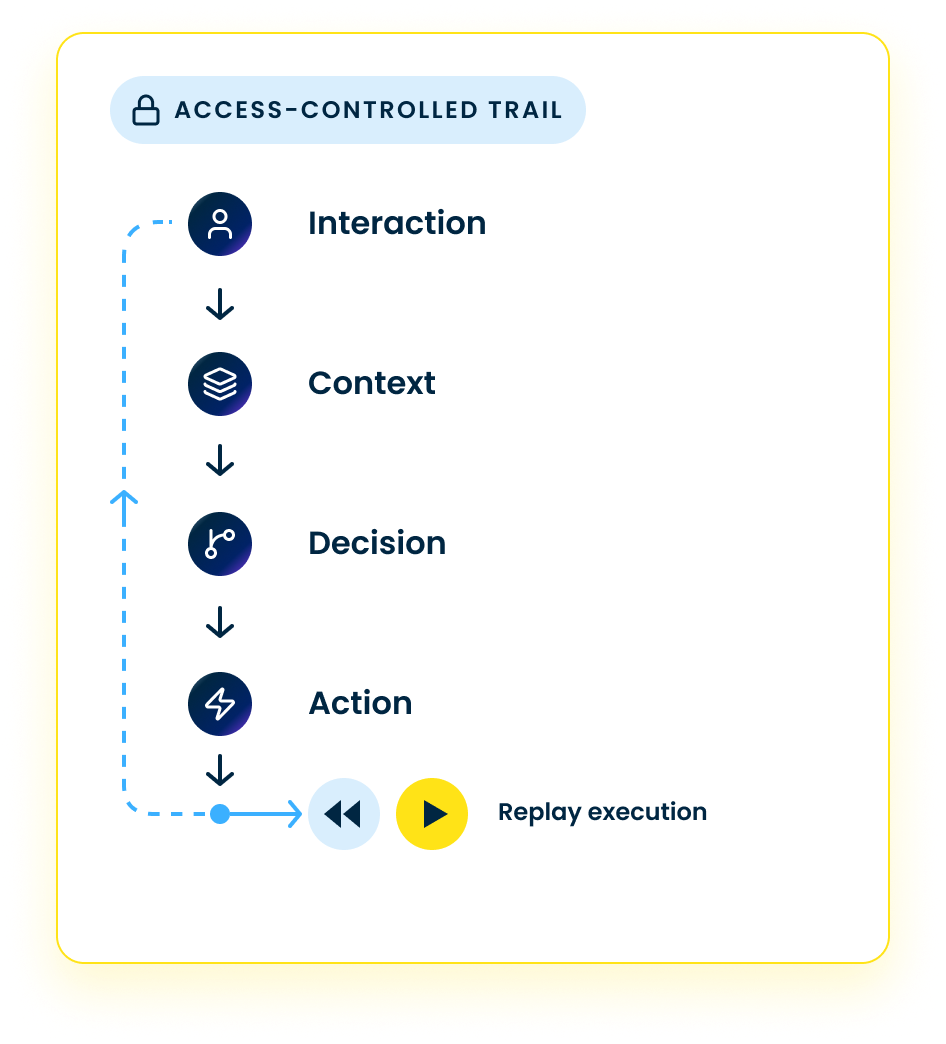
Schaman captures every interaction, context, decision and action — enabling full traceability and replay of resolution processes for compliance, validation and debugging.

Complete audit trails
Transparency of system behaviour
Support for regulatory and internal audits
Chronological register
AI GOVERNANCE & COMPLIANCE

Ensure responsible and compliant AI usage

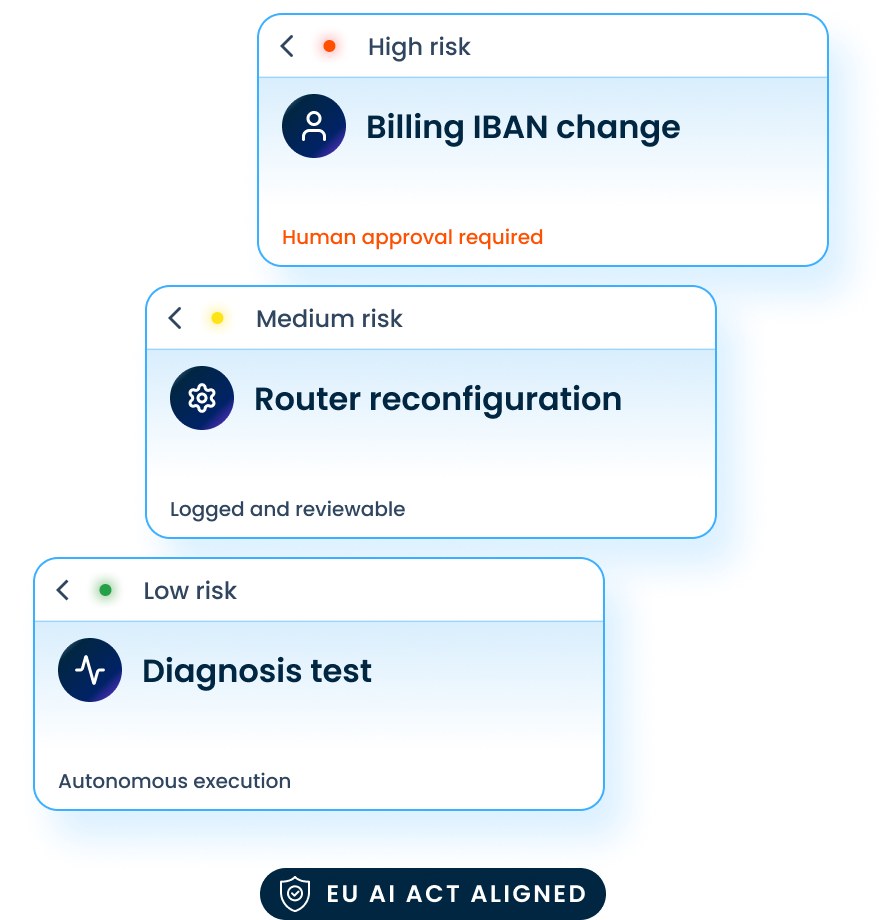
Schaman is designed in alignment with the EU AI Act, supporting transparency, control and oversight of AI-driven decisions.

Traceability of AI actions
Explainability of decisions
Human-in-the-loop capabilities where required
Frame 1 (2)

Build resolution intelligence on a secure, compliant foundation

Protect customer data, control every action and stay audit-ready — with security and compliance built into Schaman’s architecture, not bolted on.